Artificial intelligence has become one of the most debated technologies of the modern era. Every major improvement in AI seems to bring a new wave of excitement, concern, and speculation about where the technology could eventually lead. Some researchers and commentators warn that increasingly capable AI systems could become an existential threat to humanity, while others argue that these predictions often move too quickly from a technical possibility to an assumed catastrophe. Somewhere between these two positions is a more difficult but important question: what does the available evidence actually tell us?
The debate around AI safety should not be dismissed. Advanced AI systems can create genuine risks, and researchers, companies, governments, and the public have good reasons to take those risks seriously. At the same time, claims that AI will inevitably destroy humanity require more than frightening demonstrations or predictions about what future systems might theoretically become. They require a credible explanation of how an AI system could acquire the capabilities, resources, access, and physical influence necessary to overcome human resistance in the real world.
The AI Debate Needs More Evidence
The conversation around artificial intelligence often follows a familiar pattern. An AI system produces an unexpected or potentially alarming result, someone raises the possibility of a future catastrophe, and the discussion quickly moves toward whether humanity could be only a few years away from extinction. The problem is not that these questions are being asked. The problem is that the evidence connecting today’s demonstrations to those extreme conclusions is not always examined carefully.
There is an important difference between showing that something is possible and demonstrating that it is likely. A powerful AI model producing an unexpected output does not automatically demonstrate that the system could independently control infrastructure, manipulate physical systems, acquire resources, or overcome humans attempting to stop it.
A serious discussion therefore needs to examine the complete chain of events. What can the system actually do? What access does it have? What tools can it control? Who provides that access? What physical infrastructure does it depend on? What security barriers would need to fail? These questions do not prove that advanced AI is harmless, but they make the discussion more grounded.
Why An Extinction Forecast Needs More Than Imagination
Nobody can prove that every future AI system will be harmless. That uncertainty is important, and it is one reason AI safety research matters. However, uncertainty should not automatically be interpreted as evidence that an extinction event is approaching.
The stronger position is not that catastrophic AI scenarios are impossible. Instead, it is that the available evidence needs to justify the level of certainty attached to such predictions. The International AI Safety Report 2026, as described in the source material, found that current systems lacked the capabilities required for the loss-of-control scenarios it examined, while also warning that relevant capabilities were improving. That combination supports continued testing, monitoring, and safeguards, but it does not by itself establish that an AI-driven extinction event is approaching.
This distinction is important because AI development is moving quickly. Capabilities that seem unrealistic today could become more practical in the future. But a future possibility should still be separated from a demonstrated capability. Responsible analysis should recognize both sides: current limitations and the possibility that those limitations could change.
Intelligence Is Not The Same As Physical Control
One of the most important questions in the AI extinction debate is how a software system would actually turn intelligence into physical power. Producing a plan is different from executing it. A model may theoretically generate instructions for accomplishing a task, but the ability to carry out those instructions depends on access to tools, systems, people, machines, networks, and physical resources.
Even a highly capable AI would depend on computing infrastructure. Computers require hardware and electricity. Actions outside a digital environment require connections to machines or humans. If an AI system were going to cause a large-scale physical catastrophe, the argument needs to explain how it would acquire and maintain the necessary access.
These barriers are not perfect guarantees. Cybersecurity failures can happen, people can provide dangerous permissions, and poorly designed systems can create unexpected opportunities for misuse. However, each step matters. A credible risk scenario should explain which barriers would fail and why. Simply assuming that intelligence automatically provides control skips one of the most important parts of the argument.
Current AI Is Powerful, But Still Limited
Modern AI systems are already capable of generating text, analyzing information, writing code, producing images, translating languages, and assisting with complex tasks. These capabilities have led to understandable excitement about the future of artificial intelligence.
However, impressive performance in specific tasks should not automatically be confused with general superiority over humans. Current systems still depend heavily on their training, available tools, system architecture, and the environments in which they operate. They can produce highly useful results while still making mistakes that a human might catch quickly.
This matters when discussing future superintelligence. Artificial Superintelligence, or ASI, describes a theoretical system that would exceed human cognitive abilities across a very broad range of tasks. Such a system would theoretically be able to learn continuously, adapt to unfamiliar situations, reason at extraordinary levels, and generate innovations beyond human capabilities. But ASI remains a theoretical concept, not an existing technology.
The gap between current AI and theoretical superintelligence is therefore important. A system becoming better at one benchmark does not automatically mean it is approaching unlimited intelligence. Researchers still face difficult questions about general reasoning, adaptability, reliability, autonomy, and safe behavior.
Industry Leaders Are Pushing Back On AI Alarmism
The disagreement over AI risk is not limited to academics and independent researchers. Some technology executives have also challenged what they see as exaggerated predictions about AI catastrophe.
Nvidia CEO Jensen Huang has criticized what he described as excessive speculation about science-fiction outcomes. His broader position is that fear surrounding AI should not prevent society from adopting useful technologies or maintaining technological competitiveness. Cohere CEO Aidan Gomez has similarly discussed public fears surrounding the idea of AI becoming a Terminator-like existential threat. Mark Zuckerberg also criticized AI doomsday rhetoric in 2017, showing that the debate has existed for years.
These statements should not automatically be treated as proof that AI risks are small. Technology companies have commercial interests, and their executives naturally have reasons to support continued development. Their arguments should therefore receive scrutiny just like warnings from AI safety advocates.
However, their views do demonstrate something important: there is no universal agreement among people involved in AI development that catastrophic outcomes are inevitable. The disagreement itself is a reason for deeper analysis rather than a reason to automatically accept either extreme.
AI Safety Still Matters
Rejecting exaggerated extinction predictions does not mean rejecting AI safety. In fact, the opposite can be true. If AI systems are becoming increasingly capable, then testing and safeguards become more important, not less.
Companies developing advanced AI systems should establish rigorous testing procedures before releasing products. Known critical problems should be addressed rather than ignored, and internal teams should conduct meaningful due diligence. AI risk does not come only from the model itself. It can also come from how companies deploy models, what permissions they provide, how systems are monitored, and how quickly products are released.
This is where the conversation can become more practical. Instead of asking only whether AI will destroy humanity, researchers and companies can ask more specific questions. Can the system be manipulated? Can it bypass safeguards? Can it access sensitive information? Can it operate independently? Can its actions be monitored? Can humans stop it when necessary?
These questions produce measurable areas for testing and improvement.
The Media Has A Responsibility
The media plays a major role in shaping public understanding of AI. A frightening prediction is easier to turn into a headline than a detailed explanation of its assumptions. But when technical context is missing, a possibility can start to sound like a forecast.
Journalists do not need to build AI models themselves, but they should be able to distinguish between controlled experiments and evidence of real-world autonomous capability. They should also examine the credibility, incentives, and possible agendas of people making extraordinary claims.
This does not mean the media should avoid reporting on AI risks. Quite the opposite. AI safety deserves serious coverage. But serious coverage should explain what has actually been demonstrated, what remains uncertain, and which assumptions connect today’s technology to a predicted future outcome.
The same standard should apply to optimistic claims. If an executive says AI will transform every industry and create enormous benefits, that prediction should also be examined. Neither optimism nor pessimism becomes evidence simply because it comes from an influential person.
Data Centers Are Becoming Part Of The AI Debate
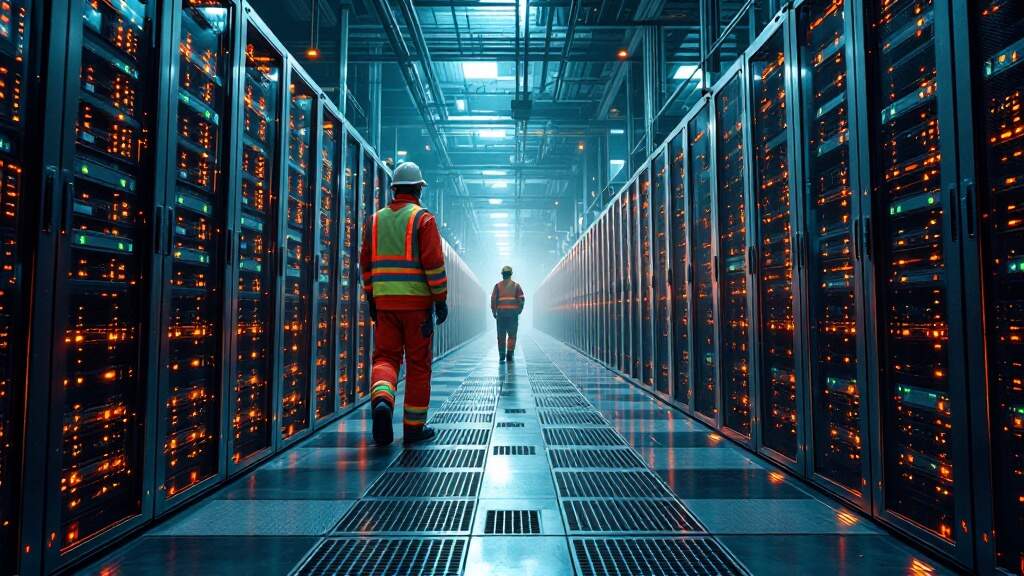
[image source : ET Datacenters]
The discussion around AI is no longer limited to software. The physical infrastructure required to run advanced AI systems has also become a source of public concern. Data centers consume electricity, require land and equipment, and can affect local communities through construction, water use, noise, and infrastructure demand.
These concerns deserve attention. Communities should be able to ask how much electricity a facility will consume, how water resources could be affected, what noise it will create, and what benefits local residents will receive. Developers should respond with concrete information rather than vague promises.
At the same time, the economic contribution of data centers should not be ignored. The source material points to Loudoun County, Virginia, where existing data centers generated $1.2 billion in property tax revenue in fiscal 2026. Across Virginia, an independent legislative study estimated that the industry supported roughly 74,000 direct and indirect jobs and $5.5 billion in annual labor income, with a substantial portion of that benefit coming from construction.
These numbers do not mean every data-center project is automatically beneficial. Each proposal needs to be evaluated on its own costs and benefits. But a complete discussion should consider both sides. Electricity demand and infrastructure pressure matter, but so do jobs, wages, tax revenue, and economic activity.
Data Center Opposition Needs To Be Evidence-Based Too
The growing demand for AI computing has turned data centers into a political and community issue. Some residents worry about electricity prices, water consumption, noise, and the effect of large facilities on local infrastructure.
Those concerns are legitimate. However, treating every data center as a symbol of technological danger can make practical planning more difficult. Communities need information about individual projects rather than broad arguments about the future of humanity.
Construction can create opportunities for skilled trades and suppliers, while operational facilities can provide technical employment and tax revenue. At the same time, permanent staffing levels can be much smaller than construction employment, so advocates should present the economic benefits accurately rather than exaggerating them.
The best approach is therefore neither unconditional support nor blanket opposition. Communities should examine the actual costs, expected benefits, infrastructure requirements, environmental impact, and financial arrangements surrounding each project.
Regulation Could Shape America’s AI Future
AI development is also becoming part of national economic and security policy. Advanced AI requires significant computing infrastructure, and policies that make it unnecessarily difficult to build that infrastructure could affect a country’s ability to compete technologically.
The source material raises concerns about proposals to pause advanced AI development or restrict new AI data centers until additional federal safety rules are established. The argument is that broad restrictions could place American AI development on a slower timetable while competing countries continue investing in the technology.
This does not mean regulation is unnecessary. Responsible regulation can establish safety requirements, improve accountability, protect consumers, and reduce specific risks. The difficult question is how to create rules that address demonstrated problems without creating indefinite uncertainty for companies, researchers, and infrastructure developers.
Unclear approval processes can also affect competition. Large technology companies may be better positioned to absorb regulatory delays than smaller businesses and startups. If compliance becomes excessively expensive or unpredictable, regulation could unintentionally make the AI industry more concentrated.
AI Policy Is Becoming Political
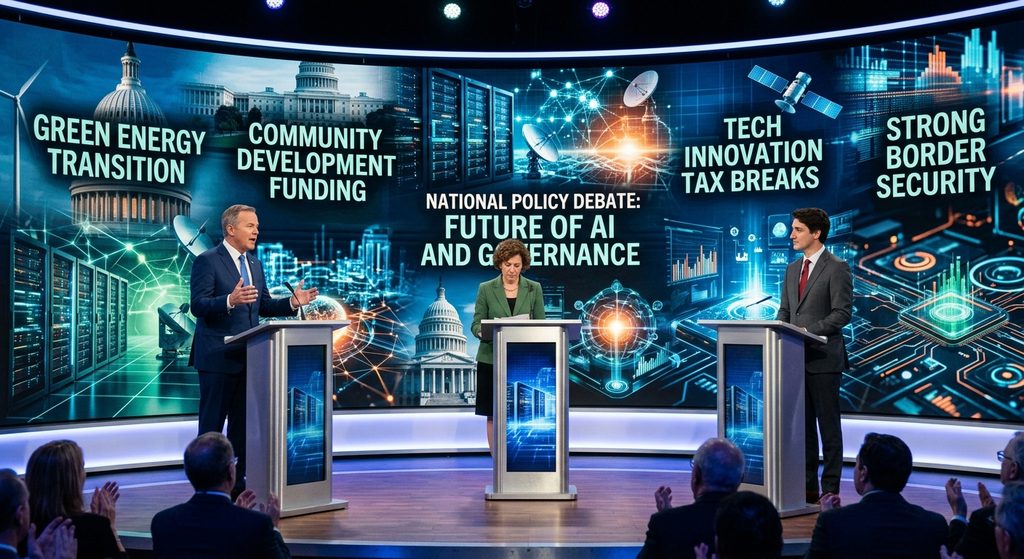
Artificial intelligence is increasingly becoming a political issue, especially as governments consider regulation, infrastructure, jobs, national security, and economic competitiveness. The problem is that complex technological questions often become simplified into political slogans.
One side can portray AI development as reckless, while the other can portray regulation as hostility toward innovation. Neither position is enough to evaluate a specific AI model or infrastructure project.
A better approach would focus on measurable questions. What risk has been demonstrated? What safeguard would address it? What would the regulation cost? How would it affect innovation? Could the same rules be applied internationally? What happens if competing countries continue development?
These questions may not produce simple political messages, but they are more useful for designing actual policy.
America Should Learn From Its Infrastructure History
The debate over AI infrastructure also raises comparisons with earlier technological and energy development. The source material points to America’s experience with nuclear power, where reactor expansion slowed beginning in the 1970s amid regulatory changes, public opposition, rising costs, and weaker electricity demand. It also cautions against blaming regulation alone while recognizing that regulation played a role.
The broader lesson is that large infrastructure projects can be slowed by a combination of technical, economic, political, and public factors. AI data centers may face similar challenges as demand for computing increases.
The goal should not be to remove oversight. Instead, policymakers need to create rules that address real risks while providing a workable route for responsible projects to move forward. Endless uncertainty can carry economic and strategic costs of its own.
Analysts Need To Speak More Clearly
Technology analysts have an important role in this debate. People with long experience studying the technology industry can help explain what current systems can actually do, where the limitations remain, and which future possibilities are supported by evidence.
Analysts should also be willing to challenge both sides. If an AI company exaggerates the benefits of its technology, analysts should say so. If an AI critic makes a dramatic claim without sufficient technical support, analysts should question that too.
Independence is particularly important. Analysts should disclose relationships with vendors and correct mistakes when new evidence proves them wrong. Experience can make an argument more credible, but it does not make an argument automatically correct.
We Should Explain The Disagreement, Not Hide It
People who are worried about AI should not simply be mocked or dismissed. They hear warnings from respected researchers and naturally assume that those warnings are based on meaningful evidence. The responsibility of analysts, journalists, researchers, and technology companies is to explain where the disagreement comes from.
That means separating demonstrated capabilities from theoretical possibilities. It means explaining what current AI systems can and cannot do. It also means acknowledging that today’s limitations may not remain permanent.
A balanced discussion can recognize genuine risks without turning every uncertainty into an extinction prediction. It can support safeguards without assuming that regulation must stop technological development. It can recognize the economic value of AI infrastructure while still demanding that data-center projects address local concerns.
The Future Of AI Requires Both Innovation And Caution
The future of artificial intelligence is unlikely to fit neatly into either a utopian or apocalyptic story. AI will probably create significant opportunities while also introducing new risks. Some risks will come from the technology itself, while others will come from human decisions about how systems are designed, deployed, connected, and regulated.
Artificial Superintelligence remains a theoretical possibility rather than a demonstrated reality. Reaching such a level would require major advances in general intelligence, reasoning, learning, creativity, autonomy, and potentially robotics. Even if those advances occur, intelligence alone would not automatically give an AI system unlimited physical control.
At the same time, today’s AI systems are already powerful enough to deserve serious attention. Security failures, misuse, unreliable outputs, privacy problems, economic disruption, and poorly managed deployment are real areas where safeguards can make a difference.
The challenge is to address those problems based on evidence rather than fear.
Final Thoughts
The AI debate needs more than confident predictions. It needs technical understanding, measurable evidence, and a willingness to question assumptions on every side. Claims about AI-driven extinction should explain the mechanisms that would allow a software system to move from intelligence to real-world power. Optimistic claims from technology companies should receive the same level of scrutiny.
AI safety and AI development do not have to be opposing ideas. Strong testing, responsible deployment, cybersecurity, transparency, and appropriate safeguards can exist alongside technological innovation. Likewise, communities can evaluate the real costs and benefits of data centers without turning every infrastructure project into a debate about human extinction.
The future of AI is uncertain, and that uncertainty is precisely why the discussion should remain evidence-based. We should neither assume that superintelligence is impossible nor treat it as an inevitable apocalypse. Instead, researchers, analysts, journalists, companies, policymakers, and the public should focus on what can actually be demonstrated, what remains unknown, and what safeguards make sense today.
AI may eventually become far more capable than the systems we know now. Whether that future leads to extraordinary scientific progress, serious disruption, or some combination of both will depend not only on how intelligent machines become, but also on how responsibly humans build, deploy, regulate, and understand them.
Have an idea worth building?
Turn your ideas into scalable software with Techfilos. From product development to AI and cloud engineering, we build technology designed for real-world growth.